Our roots are in identity. Our record is in adoption.
Enterprise identity that keeps up with the mission, from national scale to the tactical edge.
The deadline is set. The applications are not onboarded.
You have a target-level zero trust date, an approved identity provider, and hundreds of applications that still authenticate their own way. Access requests still move as forms. Coalition partners and forward sites need identity that works when the link is down. Auditors want a master user record and a clean audit. Every user, device, and non-person entity has to be uniquely identified, and now the agents you are standing up need identities too.
The technology is mostly bought. The work is adoption.
Identity is only as successful as its adoption.
At Bana, our roots are in delivering enterprise Identity, Credential, and Access Management (ICAM) systems to secure missions. We see identity as a mission enabler: it reduces friction on information sharing and keeps usability at the forefront. We measure ourselves on how many applications, users, and sites are actually on the platform, not on how many are planned.
We design, integrate, operate, and modernize identity platforms serving millions of users and thousands of applications: single sign-on and federation, phishing-resistant multi-factor authentication, risk-based identity proofing, identity governance and administration, automated provisioning and deprovisioning, self-service application onboarding, PKI and smart-card integration. Onboarding is run as an engineering discipline, with dedicated integration teams, playbooks, and a self-service marketplace, so a new application is a routine event rather than a project.
Enterprise authorization services (XACML policy, OIDC brokering, attribute synchronization) let mission applications across agencies, coalition partners, and emergency responders share data under policy, across security domains, on hybrid cloud and on-premises infrastructure. The right individual reaches the right resource at the right time, and every decision is logged.
Agentless privileged-access architecture with credential vaulting, two-factor enforcement for every privileged account, just-in-time elevation, and continuous compliance monitoring, deployed on every network of a global enterprise at every classification level. Privileged sessions are supervised, not just vaulted: the platform that grants elevation watches what is done with it and can end the session. One cross-domain deployment of a commercial platform, instead of one copy per network, is how we avoided duplicate licensing and a duplicated operations team.
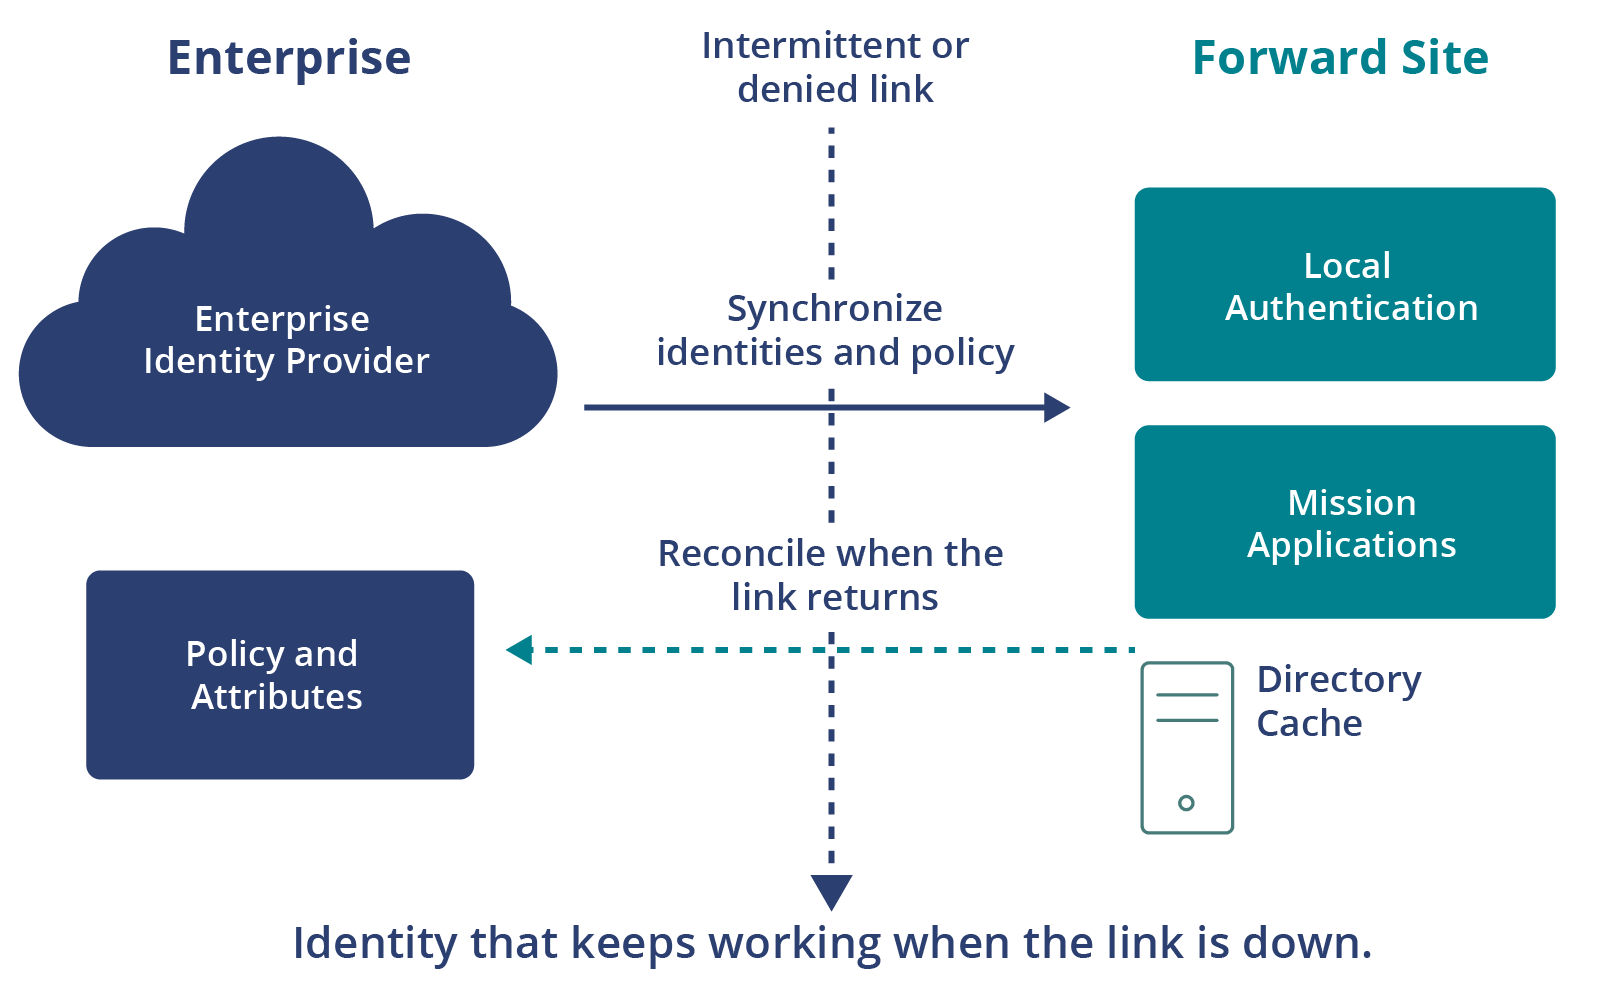
A reference architecture for forward-deployed and disconnected sites: standards-based identity synchronization with intelligent directory routing, local authentication that keeps working when the link is down, administrator-approved local registration, immutable local audit that syncs to the enterprise SIEM on reconnection, and store-and-forward messaging so no request is lost. Built for denied, degraded, intermittent, and limited connectivity and for mission partner environments.
We bring government-wide credential providers online with account linking, broker identity from the enterprise provider into applications and maps, and we have operated identity, authentication, and federation across a federal civilian department’s connected and air-gapped networks for six years.
12 in a single month
The record pace of application onboarding on a national identity platform serving more than a million users. Hundreds of applications integrated, because identity is only as successful as its adoption.
Outcomes, measured.
Identity for people, services, and agents.
Service accounts, pipelines, and AI agents outnumber the people on most networks. We give each one an identity, an owner, a baseline, and a way to be shut off.
SpecterIQ is a commercial identity threat detection platform built and supported by Bana. It learns how every identity behaves, treats AI agents as first-class identities with delegation accounting, correlates activity into campaigns, explains every alert, and responds through open standards such as Continuous Access Evaluation Profile (CAEP) and Shared Signals. We deployed a production CAEP transmitter at a federal agency, among the first in the federal government.
The platforms you have already chosen.
Okta (Identity Engine, Workflows, Terraform automation) · SailPoint IdentityIQ · Radiant Logic · ForgeRock · Keycloak · CyberArk · Active Directory and Entra ID · Experian risk-based identity proofing · Login.gov and ID.me federation · PKI and CAC · FIDO2 and phishing-resistant authenticators · XACML · OIDC, SAML, SCIM · Open Policy Agent · CAEP, RISC, and Shared Signals · Temporal · Kafka · ArcSight · Elastic
Start where you are. Strengthen every release.
We start where you are, with the platforms, policies, and people you already have, and we deliver every identity engagement the same way: Start. Ship. Strengthen. In practice that means integration engineering as a discipline, automation-first operations with infrastructure as code and containers, and continuous ATO under ICD-503 and RMF, so releases ship on a regular, agreed cadence and the authorization keeps pace. Open standards by default (OIDC, SAML, SCIM, XACML, Open Policy Agent) and no vendor lock-in, so the platform you adopt stays yours.
Governance from plain language.
We have designed and built a prototype that generates access-request workflows from plain language with a model that runs inside your boundary. It derives approvers and segregation-of-duty rules from a relationship graph rather than hand-built roles, keeps a human-readable trace for every decision, and publishes policy to Open Policy Agent enforcement points with verified parity.


