See the identity. Stop the campaign.
SpecterIQ is identity threat detection that learns how every identity behaves, human or machine.
The most dangerous attacker in your enterprise does not break in. They log in. Stolen credentials, insiders, and misbehaving AI agents look authorized to every rule-based tool you own. SpecterIQ is Bana’s commercial answer: a platform that learns what normal looks like for every person, service account, and agent, and tells you the moment one of them stops behaving like itself.
Behavior is the credential.
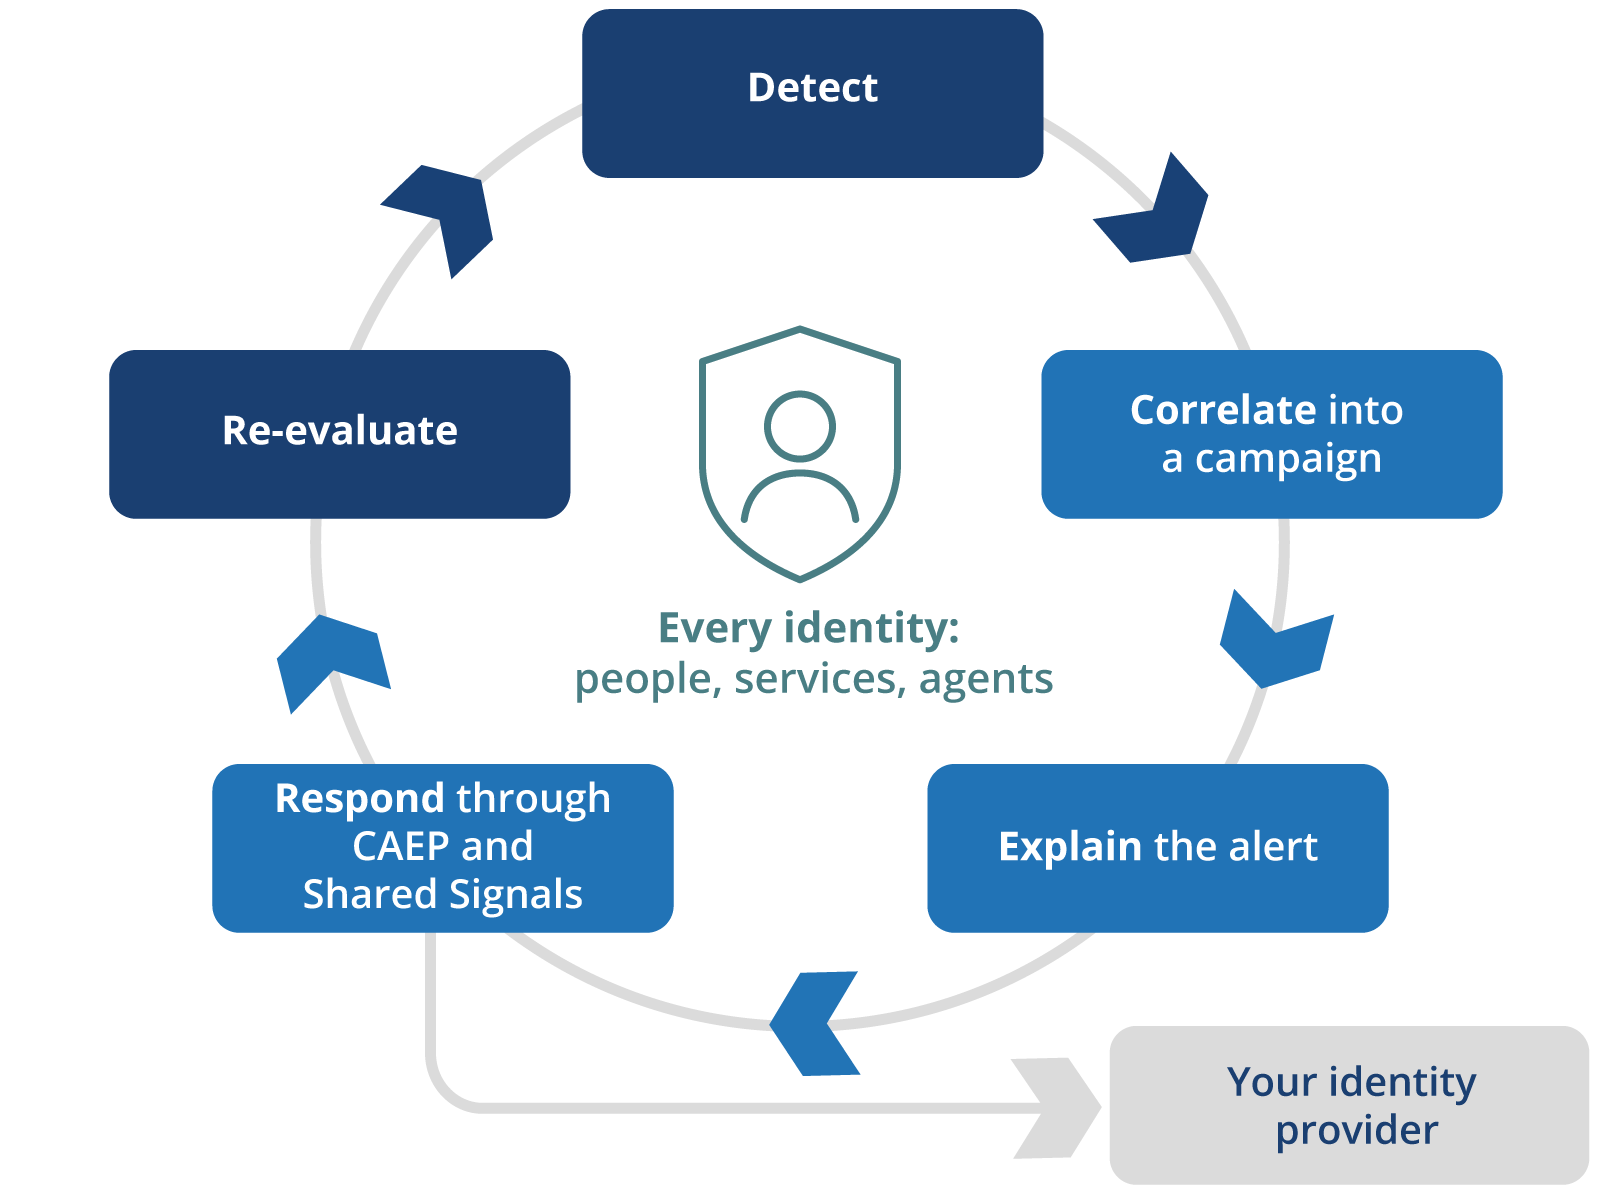
SpecterIQ streams identity and access events into a suite of graph and sequence models that build a baseline for each identity: its own history and the behavior of its peers. Anomalies roll up into entity risk and, when they share infrastructure or a path across your systems, into correlated campaigns. The privileged session is where an insider becomes damage. SpecterIQ scores that session against the identity’s own history and its peers, and can have your identity provider revoke it before it ends.
- Five behavioral detectors run continuously: unusual journey, atypical hours, access frequency, missing authentication, and high-null composition
- Peer baselines exclude the identity under review and weight by distinct peers, so one loud compromised account cannot drag the norm
- Campaigns are assembled from evidence, with kill-chain phases mapped to MITRE ATT&CK
- Every alert is explainable: per-event contributions, the journey graph, and a plain-language “normal versus this” comparison
Your AI agents have accounts. Now they have baselines.
A healthy AI agent already looks like reconnaissance: broad, fast, and tireless. SpecterIQ treats agents as a first-class identity class, baselines them only against other agents, keeps an account of whose credentials each one is acting under, and computes a shut-down, review, or normal recommendation from behavior rather than from a rule someone wrote last year.
Standards-native response. No custom glue.
When risk crosses the line, SpecterIQ emits OpenID Continuous Access Evaluation (CAEP) and RISC security event tokens under the Shared Signals Framework and opens the incident in your service-management system. Your identity provider, SIEM, and orchestration tools receive signals they already understand. That is zero trust as a loop, not a dashboard.
Deploys where your data lives.
SpecterIQ ships as Helm-deployed containers on Kubernetes, runs on EKS in AWS GovCloud, and has an OpenShift variant for disconnected and air-gapped platforms. Model tracking, drift monitoring, and metrics come with it. The dashboard carries a Section 508 assessment and a VPAT.
Proven in the hardest room first.
SpecterIQ grew out of an identity threat-detection prototype Bana designed, built, and authorized for a federal intelligence agency, and was rebuilt as a clean commercial platform in 2026. That lineage includes a production Continuous Access Evaluation transmitter, among the first in the federal government, and an ICD-503 authorization on the predecessor system.
Commercial product. Federal path.
SpecterIQ is a commercial product built and supported by Bana Solutions and available through a federal reseller. It fits inside the identity and zero trust program you already run; it does not replace your identity provider, it watches it.


